Microsoft is updating the author-signing certificate used for its NuGet packages, with the new certificate becoming the default from 23 September 2026. Developers and organisations that validate Microsoft-signed packages through NuGet client policies or dotnet nuget verify may need to update their certificate settings to avoid potential disruptions.
What You Need to Know
Microsoft uses an X.509 certificate to author-sign its NuGet packages. While existing packages will keep their current signatures, the existing certificate will no longer be used to sign new packages after the transition.
Who Will Be Impacted?
The update may affect customers who use a NuGet client policy to maintain an allow list of trusted signers that includes Microsoft. Check your nuget.config files to see whether a client policy is configured, and remember that these files can exist across multiple locations and scopes. It will also affect customers who use dotnet nuget verify to confirm that signed packages are author-signed by Microsoft.
What If Neither Applies to You?
If you don't use a NuGet client policy or dotnet nuget verify, you should not be affected by the certificate update. Microsoft NuGet packages signed with the new certificate should install the same way as packages signed with previous certificates.
If You Use a NuGet Client Policy
Add the new Microsoft certificate to your trusted signers as soon as possible, while keeping the older Microsoft certificates in your policy. Without the new certificate, packages signed with it may fail to install and return an NU3034 error. You can use the dotnet nuget trust command, available in the .NET 6 SDK and later, to update the applicable nuget.config file. You can also use --configfile <Path> to update a specific configuration file or manually add the new certificate to the existing Microsoft entry.
If You Use Package Verification
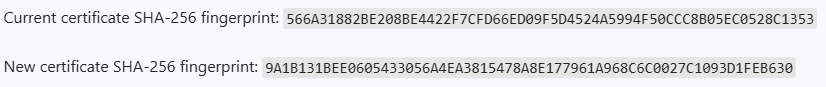
If you use dotnet nuget verify to confirm that packages are author-signed by Microsoft, add the new certificate fingerprint while keeping the existing fingerprints. Each --certificate-fingerprint option adds an accepted SHA-256 signer certificate fingerprint. Keeping all four values allows you to verify both newly signed packages and existing packages signed with older Microsoft certificates.
Build custom business applications that give your team the flexibility to work efficiently anytime, anywhere. Contact us to get started.